An explainer on CVE-2026-119085 in Virtual Engineering Workbench (VEW): how the vulnerability works, who is affected, and why redeployment to patched code is necessary according to the official bulletin.
An evidence-based editorial examining the verified facts of the Claude Code extension incident, what happened, what the evidence supports, and what remains uncertain.
An evidence-based explainer of ESC1/ESC8 intrusion paths as discussed in a Microsoft Security Blog post, focusing on help desk impersonation and AD CS abuse, and noting current evidence gaps.
An evidence-based analysis of what the Microsoft Security Blog article suggests about the CISO’s evolving role in an AI-enabled era, what remains uncertain, and how readers might interpret implications for security leadership.
An evidence-based analysis of the AWS Security Bulletin regarding missing S3 bucket ownership verification in the AWS Security Agent plugin for aws-agents-for-devsecops and MCP Server, with practical takeaway for readers.
Editorial explainer clarifying what the AWS security bulletin confirms about CVE-2026-115845 in the MCP Server run_script Python sandbox, remediation status, and usage implications for customers.
Evidence-based explainer of an AWS security bulletin detailing the PHP CVEs, affected versions, available fixes, and migration guidance, with practical reader-oriented steps and caveats.
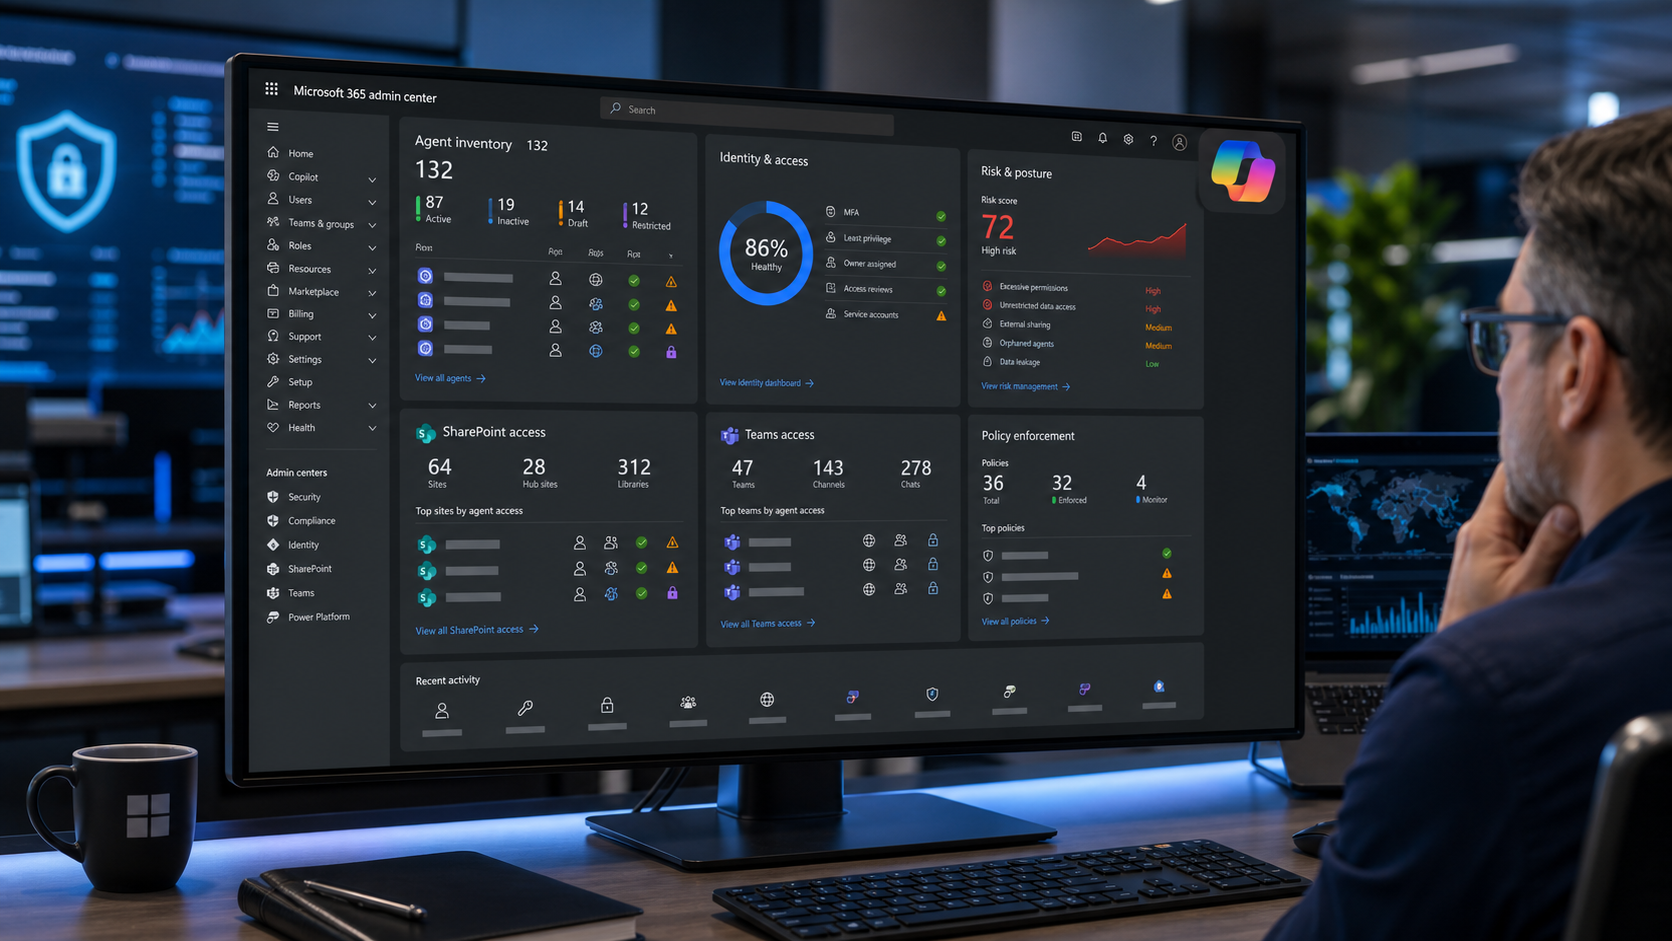
An evidence-based analysis of a Microsoft Security Blog assertion about agent insiders and the need for security to keep pace, with careful interpretation and practical, non-prescriptive guidance.
An explainer on the two CVEs in FreeRTOS-Kernel Arm Cortex-R82 MPU port, who is affected, how to remediate, and what readers should verify in their environment.
Explainer of the verified evidence on CVE-2026-110812 affecting Amazon Neptune, the patched engine versions, and the remediation steps operators should consider based on the AWS bulletin.
A Microsoft Security Blog article collects CISOs' views on how to manage vulnerability risks in the age of AI, highlighting concerns and focus areas for security leaders.
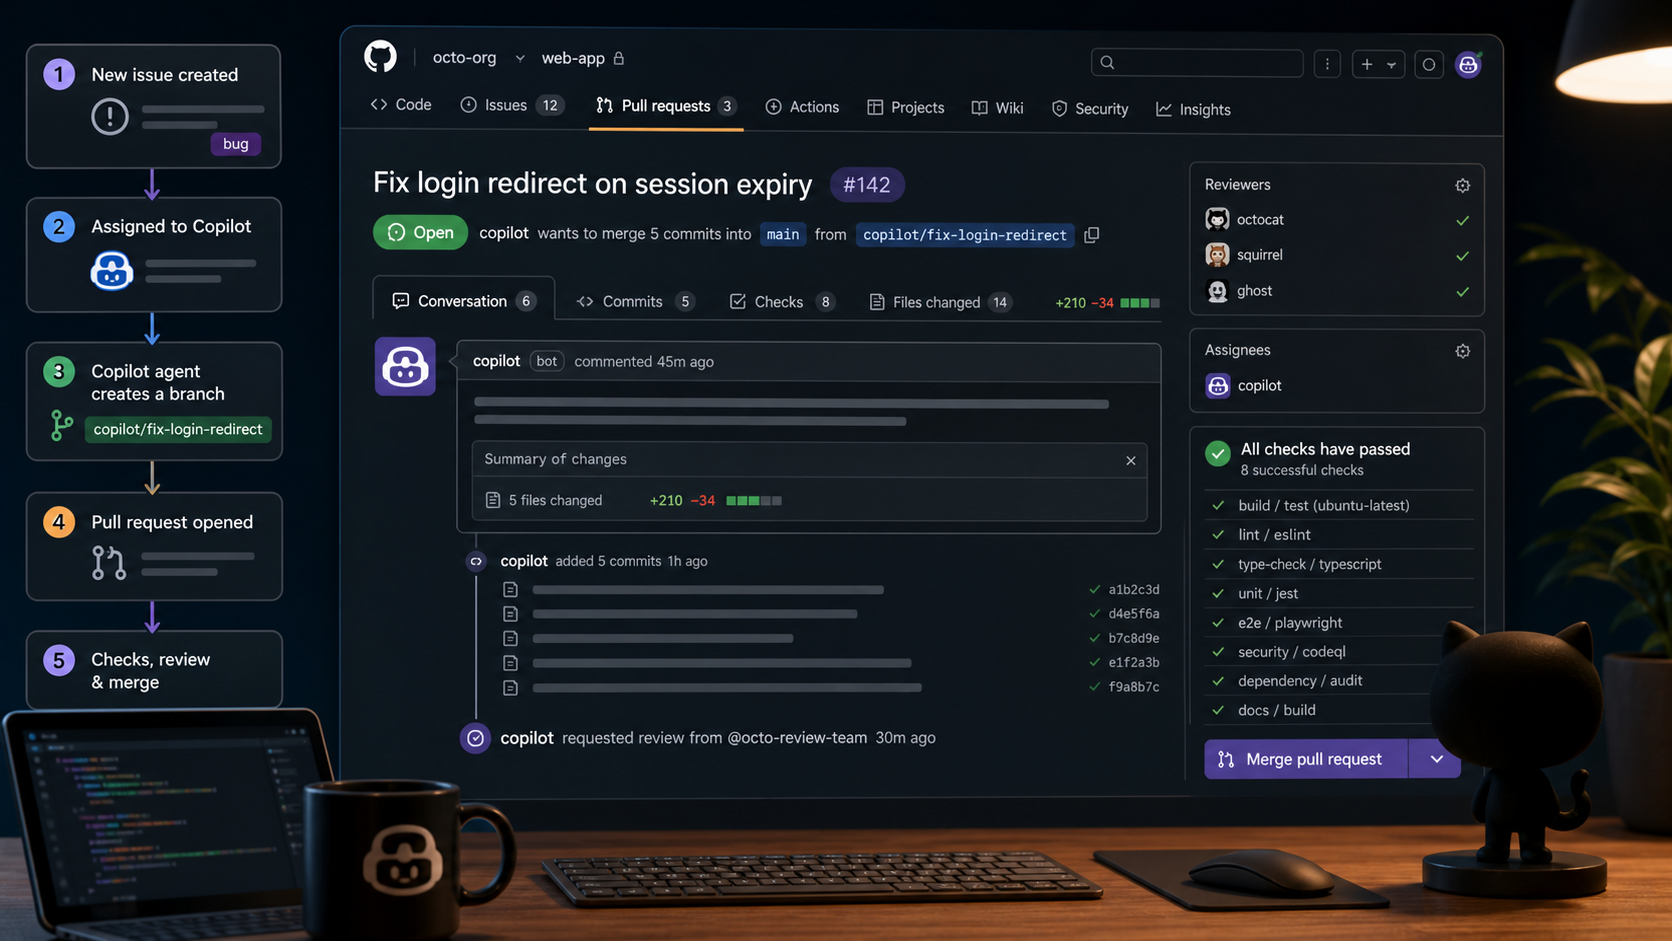
GitHub is holding potentially malicious workflow runs in public repositories for approval, adding friction where compromised credentials can steal CI secrets.
Meta is rolling out an AI support assistant for Facebook and Instagram account issues. Businesses should watch recovery controls, escalation, and fraud resistance.